Role Security
OJS Editor Access Control
Granular Role Security & Managerial Access Control for Editorial Teams
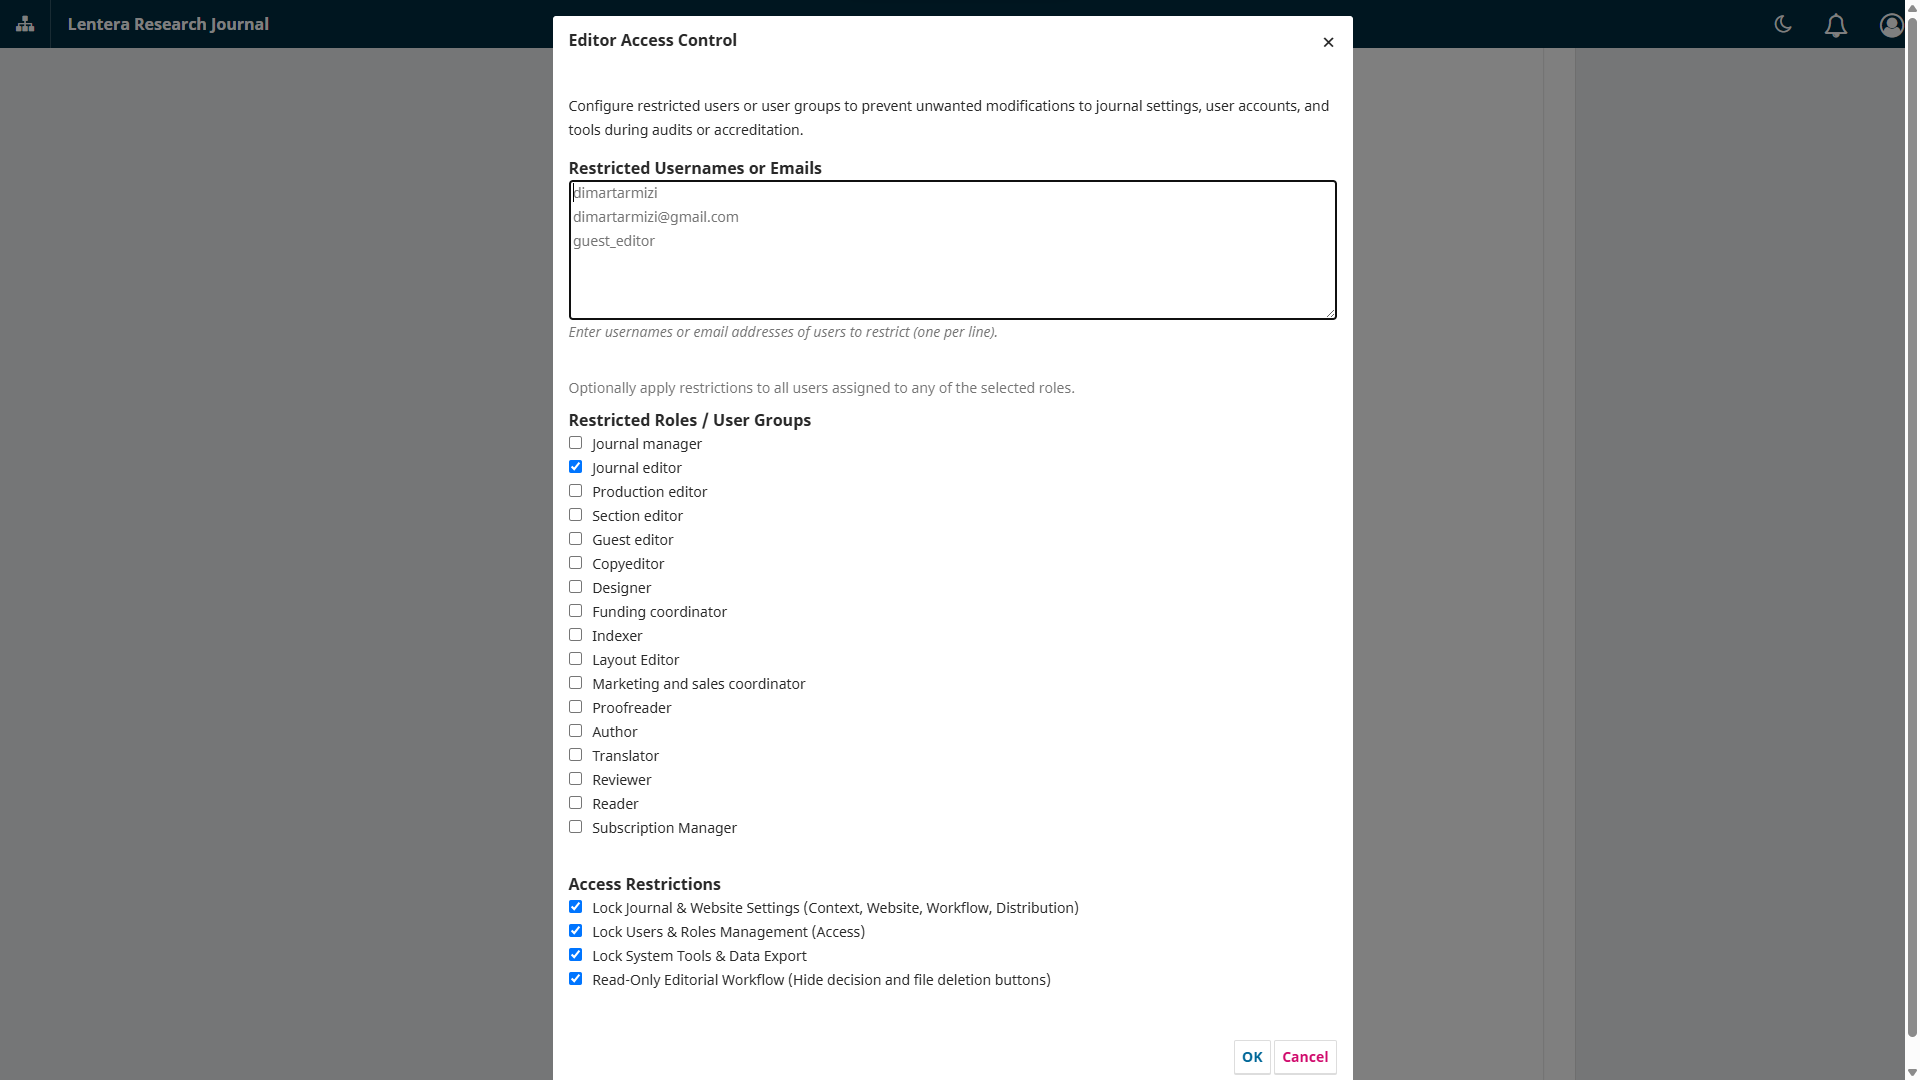
OJS Editor Access Control separates editorial workflow privileges from sensitive system settings. Editors can manage manuscripts freely without altering core journal configurations or impersonating other users.
Free
Full compatibility with OJS 3.x
Complete installation & configuration guide
Follows PKP OJS security best practices
PLUGIN PREVIEW
KEY FEATURES & CAPABILITIES
Access Control
- Lock Settings, Plugins, and Users & Roles menus for designated roles
- Retain full access to Review, Copyediting, and Production workflow stages
- Flexible role configuration managed by Site Administrators
Account Security
- Block "Login As" (User Impersonation) capability for non-administrators
- Prevent unauthorized privilege escalation within journals
- Protect the integrity of payment and email configurations
Portal Governance
- Ideal for university journal portals managing multiple editorial teams
- Compatible with OJS 3.x security standards
- Zero modifications to core OJS database tables
TECHNICAL SPECIFICATIONS
Supported PKP OJS VersionsOJS 3.x
PHP VersionsPHP 8.0 / PHP 8.1 / PHP 8.2 / PHP 8.3
Deployment MethodDownload & Install via GitHub Repository
OTHER PLUGINS
Back to Plugin Catalog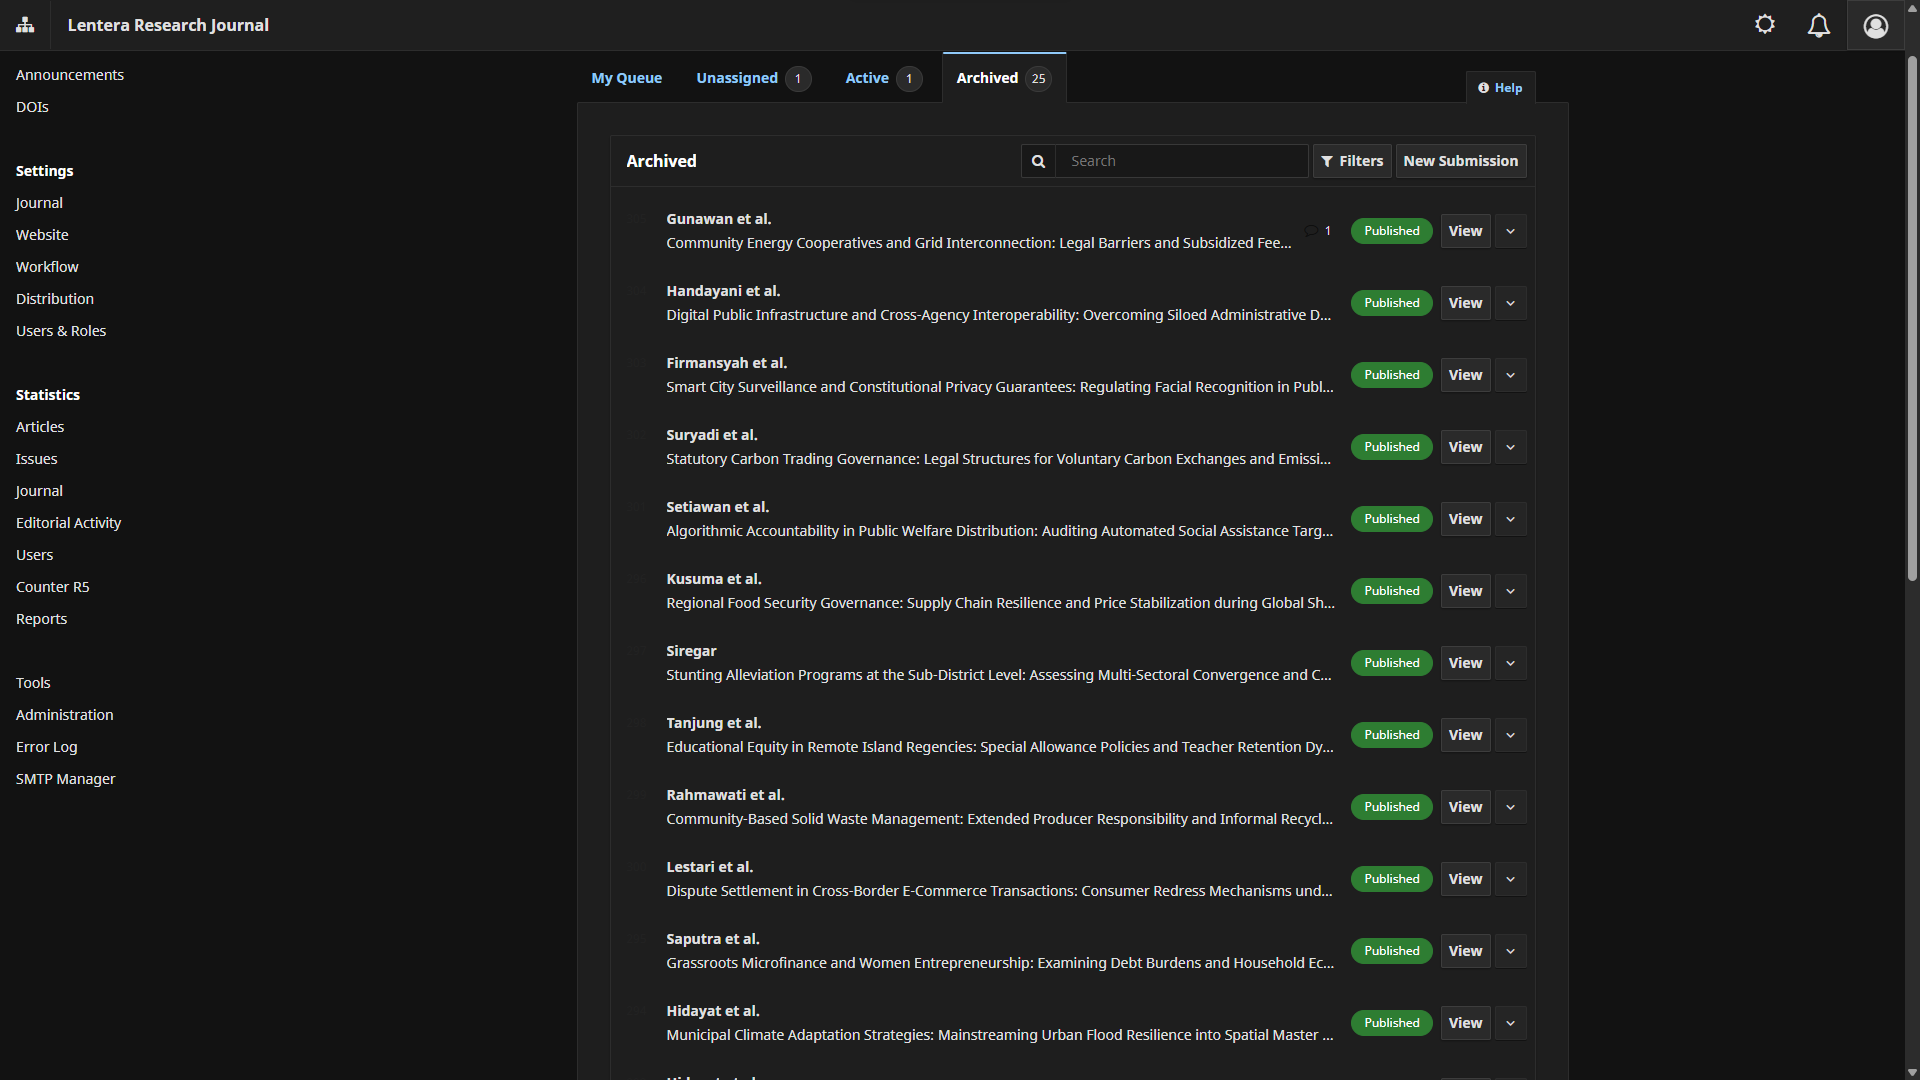
Editorial UI
OJS Dashboard Dark Mode
Sleek dark mode theme for OJS editorial dashboard, reducing eye strain during long editorial reviews.
FreeView Details
Workflow Tracking
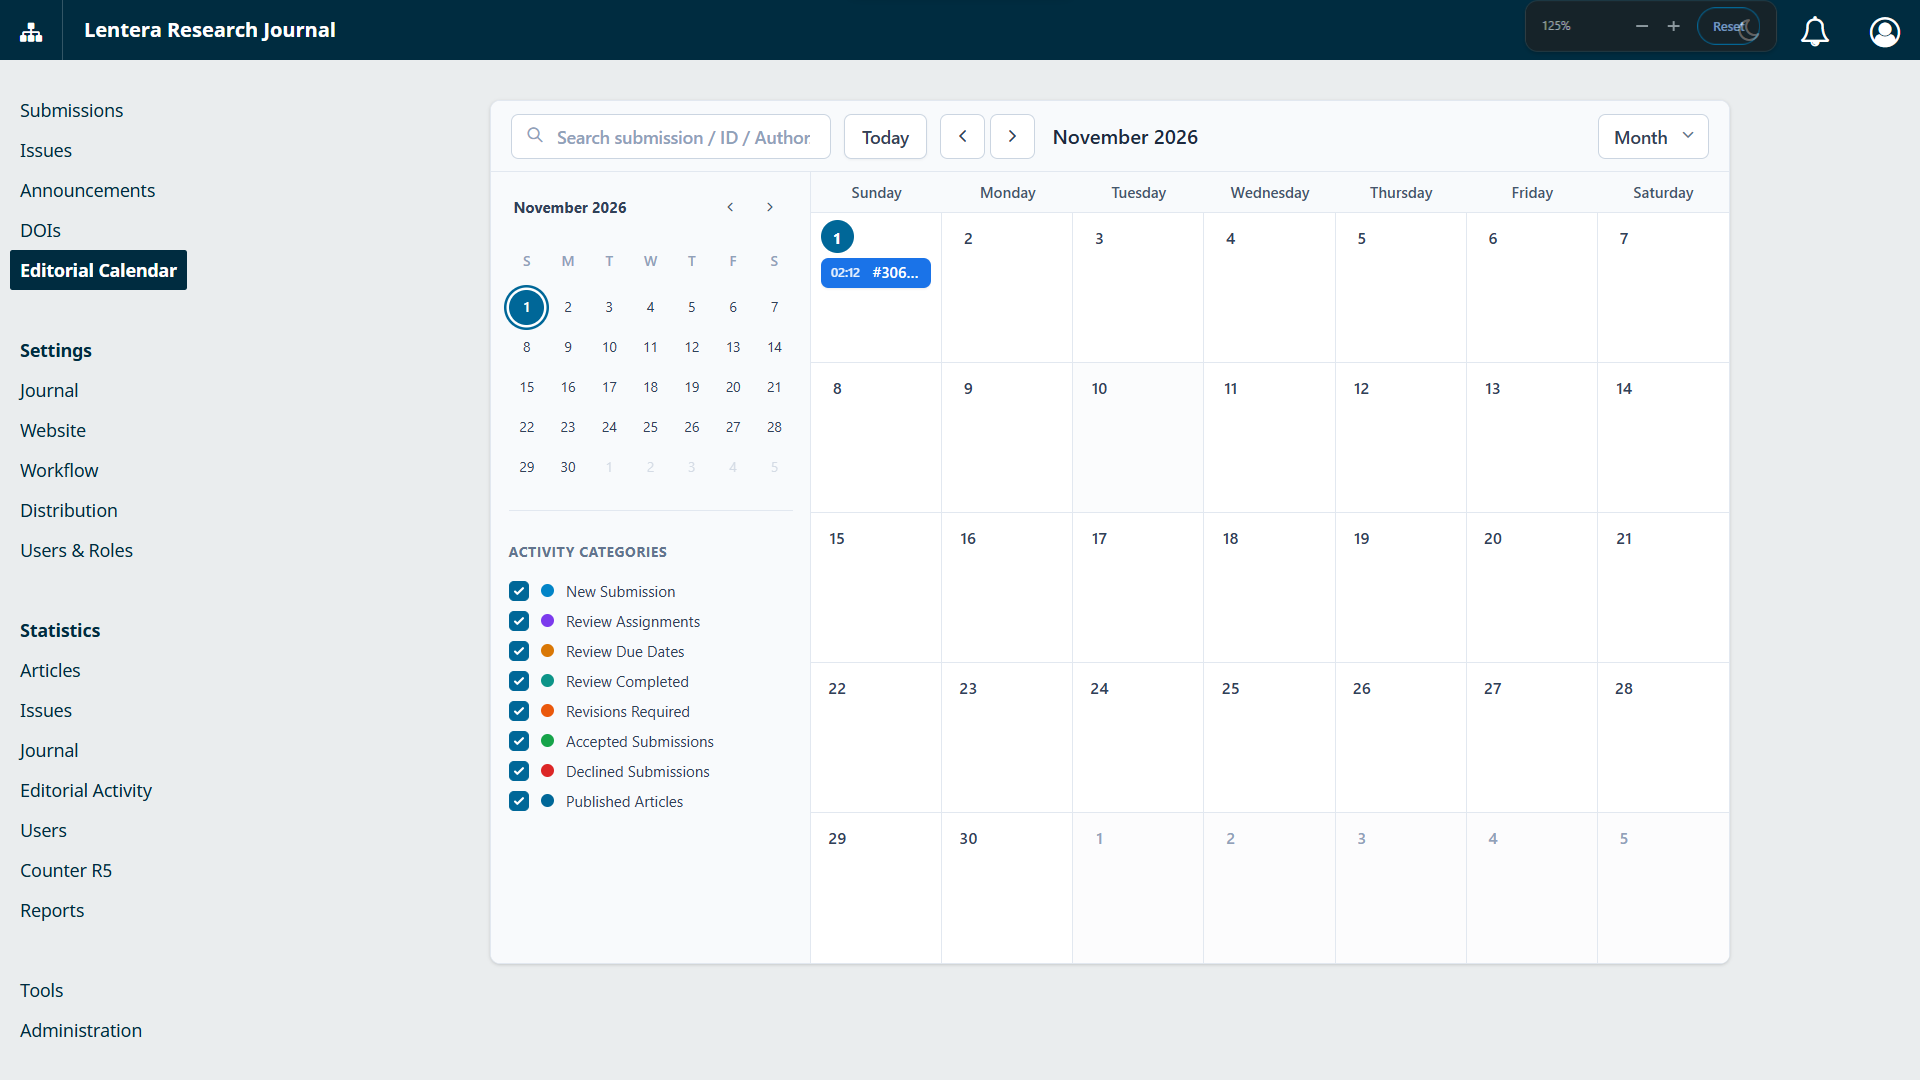
OJS Editorial Calendar
Visual editorial activity calendar allowing journal editors to track deadlines, review progress, and issue release targets.
$29View Details